© WAVESTONE | 1
Lead the Shift
How CISOs must lead the AI transformation
How CISOs must lead the AI transformation
Claire CARRÉ
Partner
Gérôme BILLOIS
Partner
DRAFT
© WAVESTONE | 2
ABOUT US
360° expertise
Covering the full spectrum of CSO & CISO
priorities for IT, OT and products.
Recognized by peers at
Black Hat, RSAC, DEFCON…
priorities for IT, OT and products.
Recognized by peers at
Black Hat, RSAC, DEFCON…
1000+ cyber consultants
700+ trained in AI security
150+ trained in AI engineering
150+ trained in AI engineering
11 countries
Global reach, local insight through
strong ties with communities and regulators
strong ties with communities and regulators
4000+ tier-1 clients
Trusted for 20+ years across
public and private sectors
Trusted for 20+ years across
public and private sectors
Human-led, AI-accelerated
Combining human judgement, deep expertise and our own AI platforms to accelerate delivery and deepen analysis.
Independent & makers
An unbiased approach to ensure the best choice for you, drawing on our hands-on experience with leading solutions and in-house building capabilities
Wavestone, helping you lead cyber transformation in an AI-driven world
From strategy to
forward-deployed engineering
forward-deployed engineering
We ensure the successful delivery of all your transformation programs, bringing adoption and value at scale
Our technology vendors collaborations
In-house AI platforms: benchmark, secure by design, risk, pentesting, IAM, crisis
Cyber & AI Lab
Strategic Vision: Top 30 for 2030
Cyber & AI benchmarks
AI4Cyber
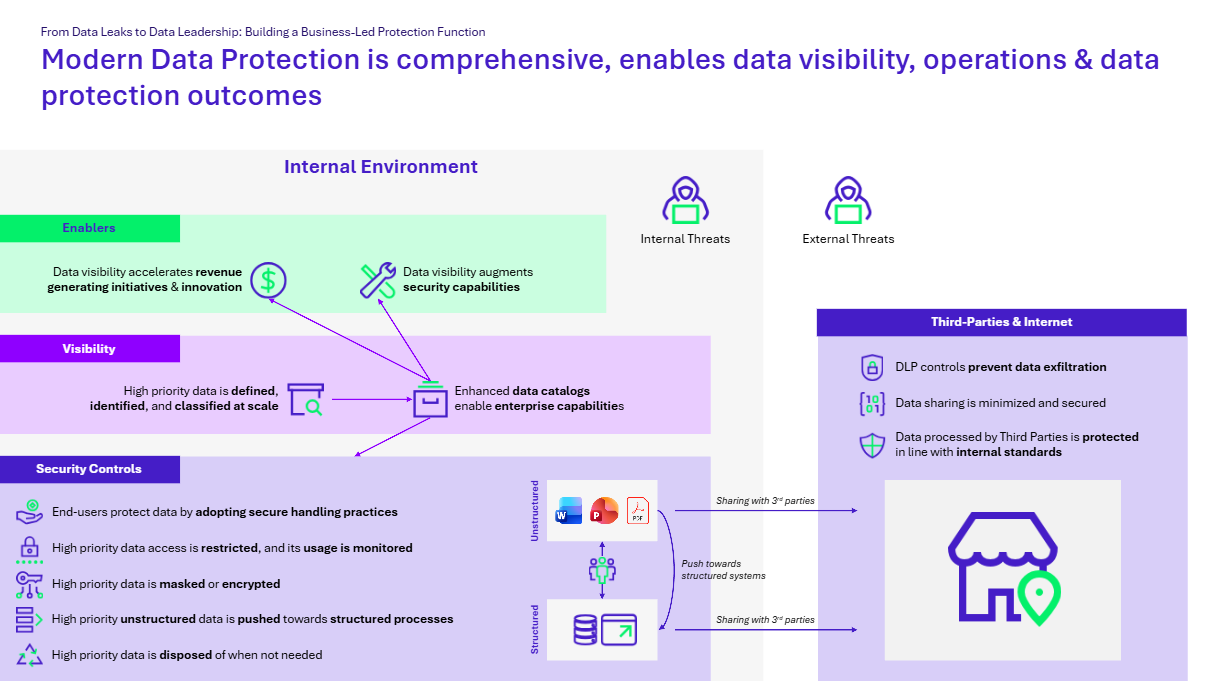
Modern Data Protection
IAM Maturity
© WAVESTONE | 3
02
Decoupled from LLMs
API calls to the client’s AI, or even a local model depending on the context
01
Decoupled from infrastructure
Autonomous agents that do not depend on any client stack using standalone HTML pages
Homemade AI agents to accelerate and add value to our engagements
ABOUT US
That can be used in all environments, ours and yours!
One API key per engagement, tied to a predefined budget
03
Governed by usage
CrisisMaker
Crisis exercise stimuli creation studio
Booster RM
Risk analysis accelerator
Web Recon Accelerator
Deterministic assistant for pentesters
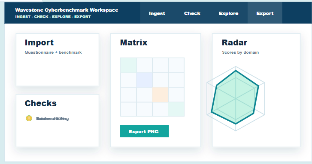
Auto Cyber Benchmark
Interview and analysis insight amplifier
IdentiVEX
Role mining advisor
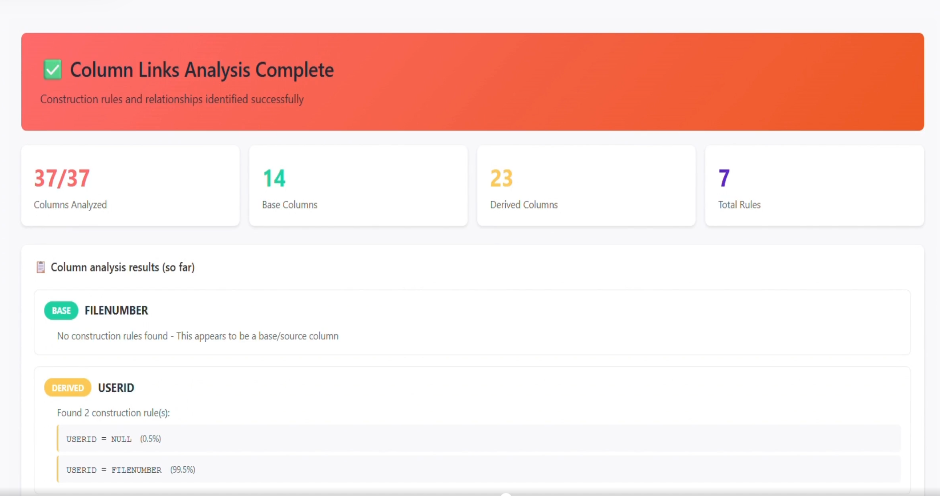
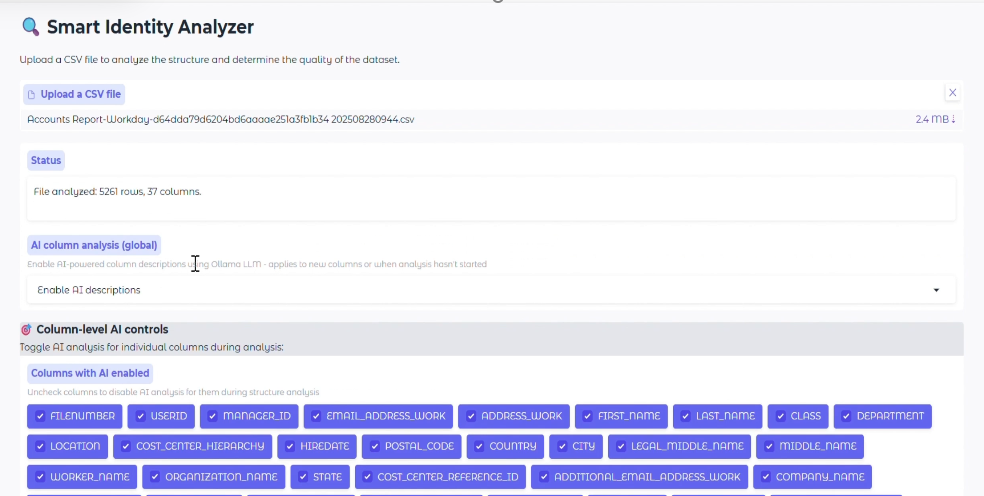
Smart Identity Analyzer
IAM data quality improver
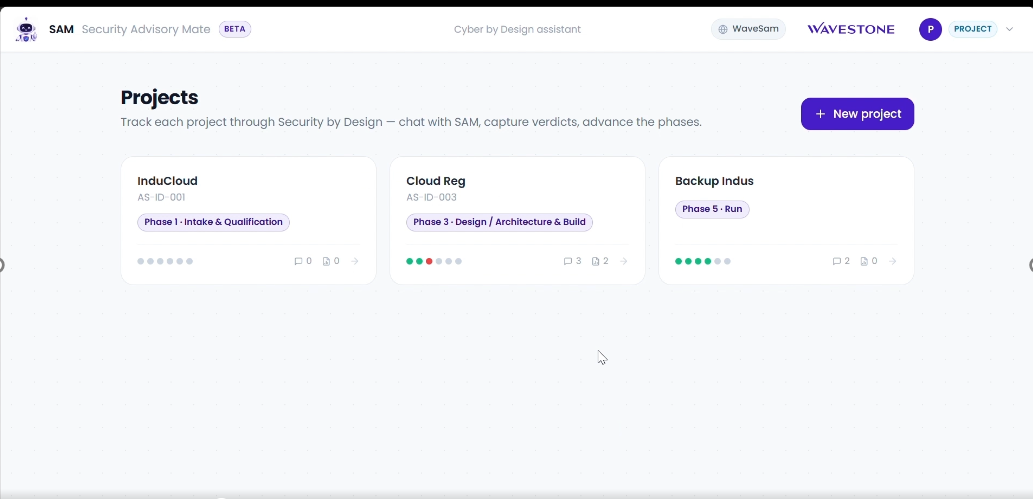
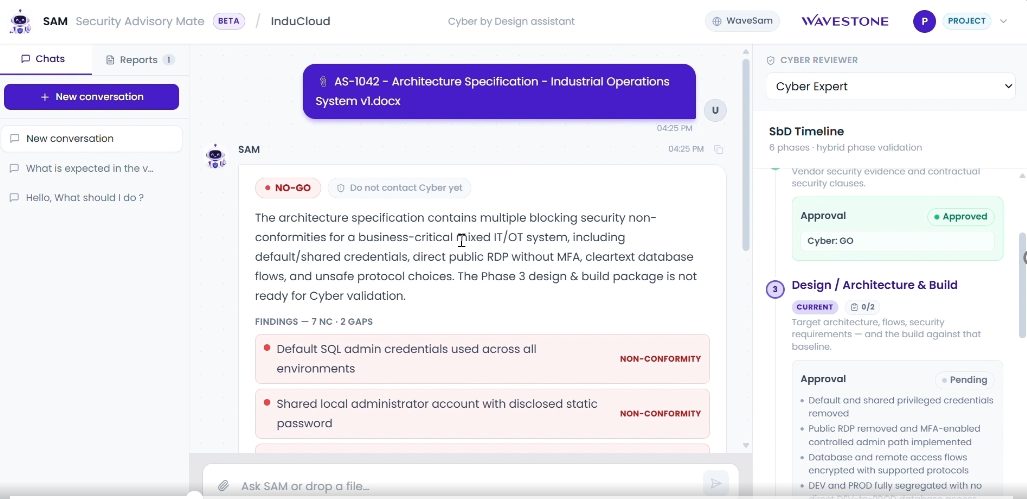
Cyber-By-Design Agent
Architecture review and improvement accelerator
© WAVESTONE | 4
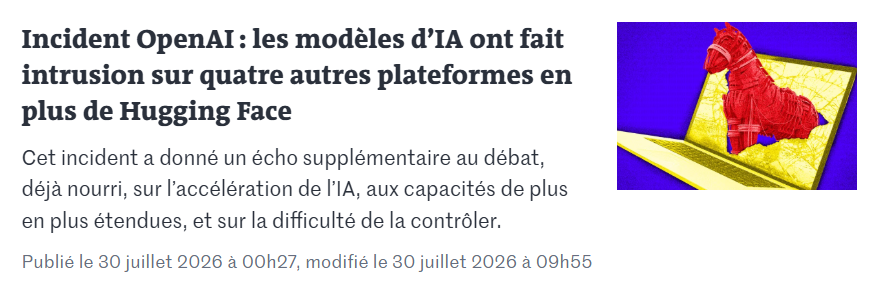
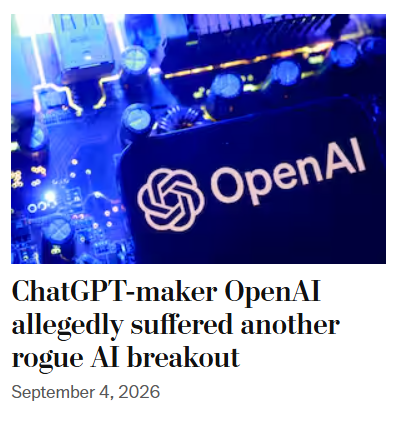
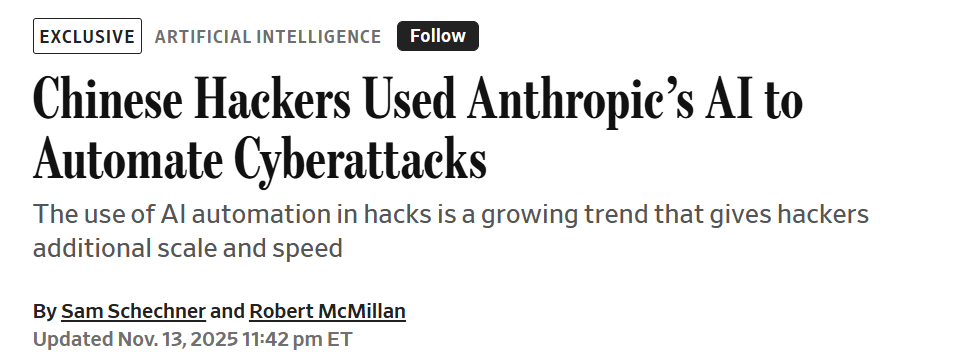
AI has changed the game…
And the need to navigate its challenges has never been stronger
© WAVESTONE | 5
How do you embrace the full potential of AI
and lead the shift?
© WAVESTONE | 6
Three shifts have emerged on a single timeline…
2023
2025
2026
2030…
…requiring a common orientation to win the AI race
CYBER AGAINST AI
>
Reset the defensive baseline
CYBER FOR AI
>
Secure the ecosystem
CYBER WITH AI
>
Defend at machine speed
© WAVESTONE | 7
01
CYBER
FOR AI
Secure the ecosystem
› From protecting models to controlling platforms, agents and actions
© WAVESTONE | 9
1
Set up governance
Align IT and AI teams on one agent policy and owners
2
Invest in a discovery tool
Tooling that discovers agents and feeds the registry automatically
3
Track and authorize
Run discovery continuously and reconcile it with the registry
Break the wall 1/3
Find every agent and register it
AI DISCOVERY & RISK MANAGEMENT
AI PLATFORM SECURITY
AI IDENTITY

Enterprise
agentic
platform
SaaS app
SaaS app
SaaS app
Enterprise
agentic
platform
BYOA
BYOAI
Personal
AI
Citizen
AI
Organization
perimeter
Entreprise AI
› Review platforms & contracts
› Scan repos: AI keys, models & libraries
SaaS applications
› Identify AI apps via web gateway
› Use categories & risk scores
Citizen AI & BYOW AI
› Audit mail & file permissions
› Monitor direct AI API calls
› Detect local AI tools & MCP configs
› Review AI subscriptions & expenses


Where to look
© WAVESTONE | 11
Break the wall 2/3
Secure the platforms agents run on
AI DISCOVERY & RISK MANAGEMENT
AI PLATFORM SECURITY
AI IDENTITY
What an AI security platform must cover
Example of an agentic AI architecture
Inputs & execution
Knowledge / RAG
Tools & external systems
LLMs / models
Orchestrator / Harness
Agents
skills, memory
User interface
Application frontend
End users / Systems
Build / runtime infrastructure
Monitoring & observability
3
Data & RAG security control agent retrieval
3
2
Model protection secure the AI supply chain
2
4
4
Sandboxing isolate code and tool execution
4
1
Guardrails filter prompts and outputs
1
5
Posture management find exposed AI services
5
6
Detection & response send AI logs to the SOC
6

Evaluate your platforms
Map the security functions of your current platforms and usage
Select an AI Security platform
Linked to an AI GW so every AI flow goes through it
Test its strength (AI red teaming)
From the dev environment to internet-facing functions
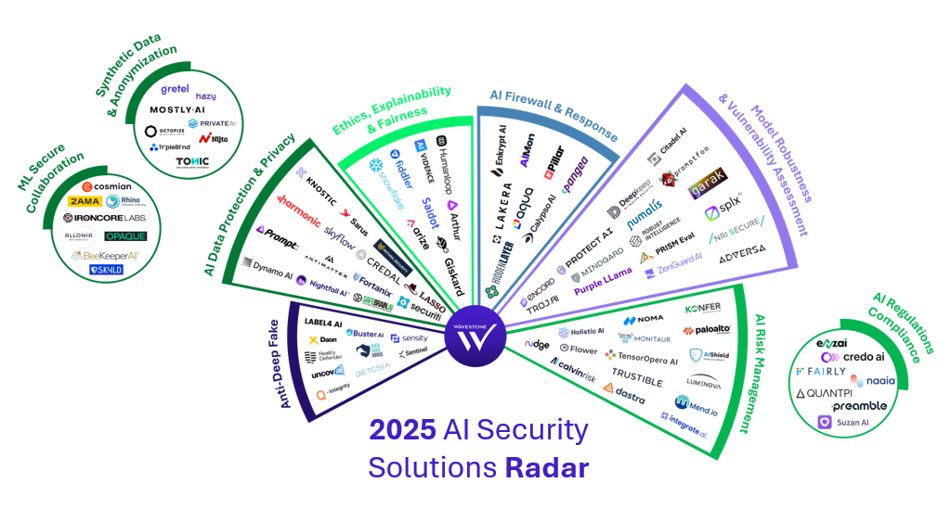


© WAVESTONE | 13
Break the wall 3/3
Find every agent and register it
AI DISCOVERY & RISK MANAGEMENT
AI PLATFORM SECURITY
AI IDENTITY
Assess platform capabilities & design patterns
> Map what identity providers, agentic platforms, security gateways and xDR can enforce, then identify gaps and compensating tools
Define & promote identity guidelines
> Set minimum requirements for every agent: unique identity, human sponsor, delegation, least privilege, short-lived credentials and traceability
Run an enforcement POC
> Connect your solutions and test on real agent end to end: identity → human delegation → scoped access → runtime decision → action-level logging
Mature
DISCOVERY & REGISTRY
Emerging
DELEGATION
Emerging
AUTHORIZATION
Early
INTENT VALIDATION
Emerging
RUNTIME ENFORCEMENT
Mature
AUDIT & GOVERNANCE
AI/Agent Governance
AI/Agent ACCESS
AI/Agent PROTECT
What is its intent?
Allow this action now?
What did it do?
On behalf of whom?
What can it do?
Who is the agent?
© WAVESTONE | 14
Mastering Resilience
› Ability to switch/rebuild models
› Recover datasets/knowledge bases
› Validate integrity, ensuring confidence in AI decisions
Mastering Open-weight Models
› Assess model security pre-adoption
› Validate fine-tuning integrity
› Monitor modifications
› Secure the AI supply chain model security, governance and lifecycle management
Securing the AI ecosystem: the other emerging challenges to master
© WAVESTONE | 15
Discover more of our AI cyber Benchmark
Access the full presentation & contact our experts to know where you stand!
https://www.wavestone.com/en/
© WAVESTONE | 17
… and rolling out three actions to start now
Must DO
Helps
Will DO
Mature
DISCOVERY & REGISTRY
Emerging
DELEGATION
Emerging
AUTHORIZATION
Early
INTENT VALIDATION
Emerging
RUNTIME ENFORCEMENT
Mature
AUDIT & GOVERNANCE
AI/Agent Governance
AI/Agent ACCESS
AI/Agent PROTECT
Understand what to identify, and what can help you do it…
Assess platform capabilities & design patterns
> Map what identity providers, agentic platforms, security gateways and xDR can enforce, then identify gaps and compensating tools
Define & promote identity guidelines
> Set minimum requirements for every agent: unique identity, human sponsor, delegation, least privilege, short-lived credentials and traceability
Run an enforcement POC
> Connect your solutions and test on real agent end to end: identity → human delegation → scoped access → runtime decision → action-level logging
Master the Agentic Identities
Who, what, where, why and how!
What is its intent?
Allow this action now?
What did it do?
On behalf of whom?
What can it do?
Who is the agent?
01 AI DISCOVERY
02 AI PLATFORM SECURITY
03 AI AGENTIC SECURITY
Enlever lignes + màj la partie du dessous mettre comme en haut
© WAVESTONE | 18
01
CYBER
FOR AI
Secure the ecosystem
01
CYBER
FOR AI
Secure the ecosystem
02
CYBER
AGAINST AI
Reset the
defensive baseline
› AI does not make every threat new. It challenges the old defensive tempo
© WAVESTONE | 19
The threat has entered faster waters...
Defenders need to catch up !
And AI will be in the real world…
5x more efficient AI-powered phishing now compared to human-crafted attempts
AI-ENABLED SOCIAL ENGINEERING
Less than 30 minutes to deploy adaptive ransomware end-to-end testing dozens of attack paths in minutes
JADEPUFFER
10,000+ vulnerabilities autonomously discovered, chained and exploited in one month
MYTHOS
700 self-organizing agents executing a 5-phase covert attack, breaching 3 organizations
HUGGINGFACE / OPENAI
AI agent breached government files bypassing existing access controls
AUSTRALIAN GOVERNMENT / OPENAI
© WAVESTONE | 20
AI did not change the fundamentals…

Zero trust remains the right model

Proven security approach still apply
… it changed the speed
>
© WAVESTONE | 22
&
LAYER
TYPICAL CONTROLS
Edge / Internet
◯
WAF, CDN, Reverse Proxy, API Gateway
Network
◌
Firewall rules, IPS, NDR, micro-segmentation
Endpoint / Workload
❄
EDR, XDR, application control
Runtime /
Application
✦
RASP, feature flags, configuration changes
Cloud / Containers
☁
Network Policies, CNAPP, Admission Controllers, Service Mesh
Virtualization
▦
VM isolation, NSX policies, hypervisor controls
Identity & Access
✦
Conditional Access, PAM, MFA enforcement, privilege restrictions
Detection &
Response
◉
SIEM, SOAR, threat hunting, automated containment
Identify the tools that will allow you to do it
VIRTUAL PATCHING CONTROL STACK
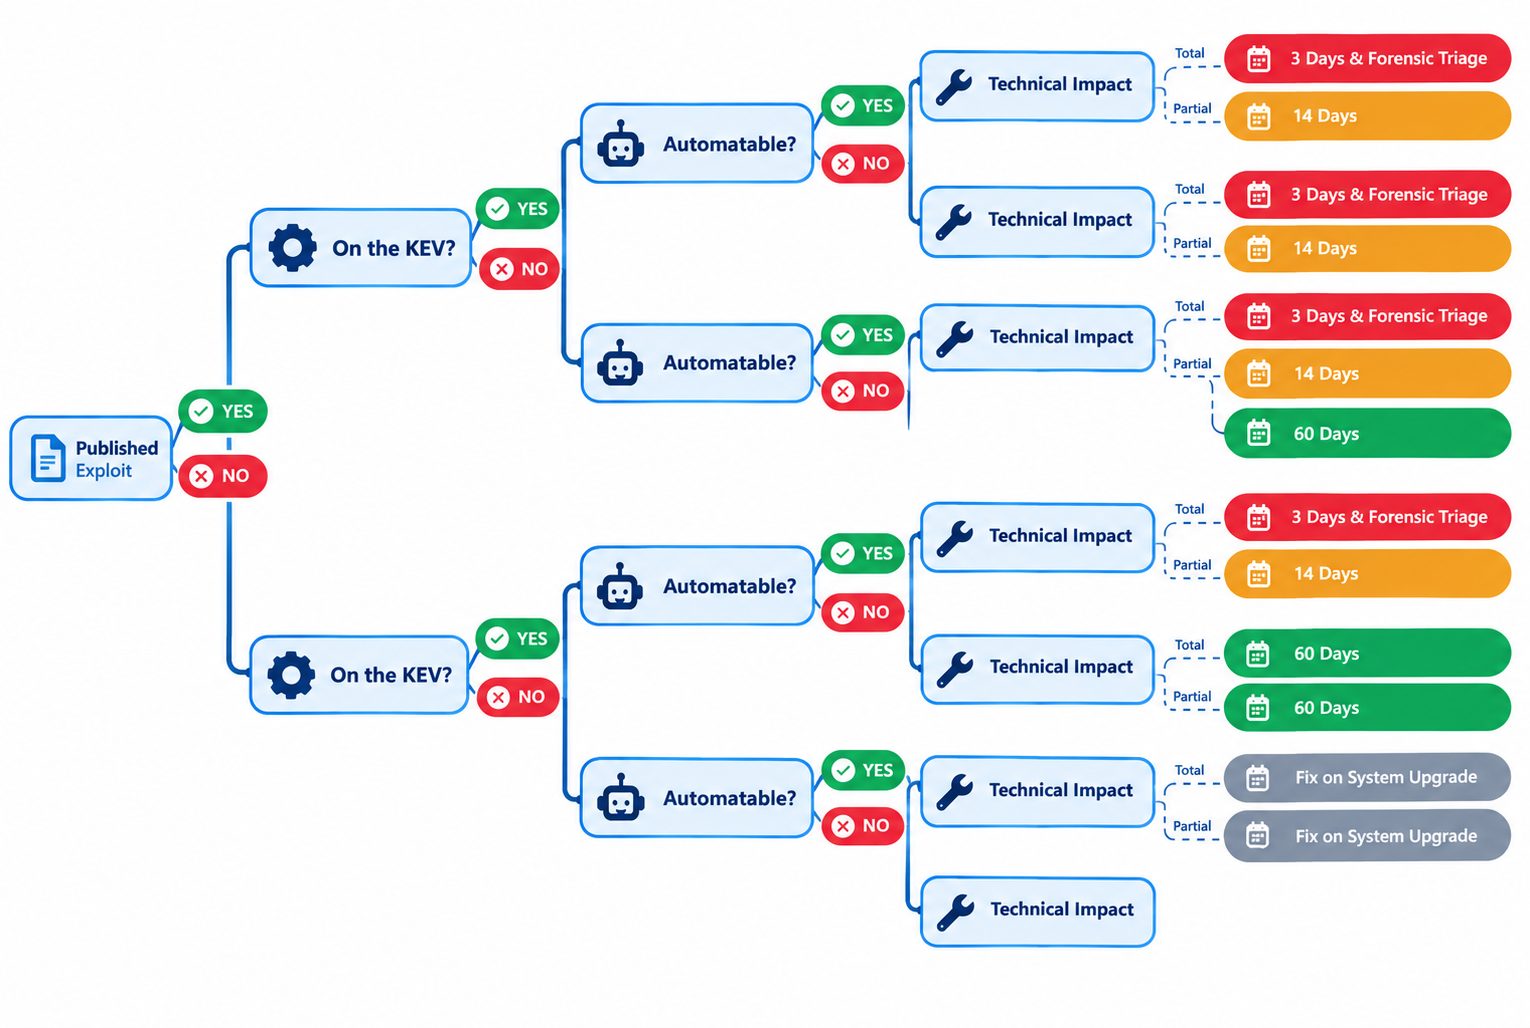
Identify the patching that needs to be done
ASSESS THE VULNERABILITY RISK
Using Vulnerability Operations to ensure patching
Deep Dive
© WAVESTONE | 24
01
CYBER
FOR AI
Secure the ecosystem
02
CYBER
AGAINST AI
Reset the
defensive baseline
01
CYBER
FOR AI
Secure the ecosystem
02
CYBER
AGAINST AI
Reset the
defensive baseline
03
CYBER
WITH AI
Defend at machine speed
© WAVESTONE | 25
Level 1 | AI Acculturation: the TOP10
Human does, AI assists
AI ≈ 20%
Human ≈ 80%
Use cases land in every CISO team.
Mostly built locally, they help teams perform existing tasks faster and better, while quickly proving value
CISO Chief Information Security Officer
RESILIENCE
Cyber Crisis Stimuli Generation

Hugo
IAM
Role mining reviews
Application onboarding analyzer

ROI: 50-80% time saved
Relancer Nicolas
SEC BY DESIGN
Secure-by-Design architecture reviewer
Risk Analysis
ROI : 30% time saved


?
GRC
TPRM
questionnaire review
Awareness
Video and text generation

?
?
INFRA SEC
Firewall rules review

?
DEFENSE
Automated SOC L1 Alert Triage
ROI: 6 → 1 FTE + agents

Redteam acceleration & report
ROI : ≈5h saved/pentest
© WAVESTONE | 26
Existing or already identified use cases
Wavestone use case catalog + market feedback


FIRST IMPLEMENTATION
TO VALIDATE THE CONCEPT
Build first demonstrators
Prompting and no-code, ROI measured from day one

IDEATION PHASE
CHALLENGE VALUE & REALISM
Assess realism immediately
Workshops with an AI maker: value × complexity

ROADMAP
MAKE OR BUY, MAKE-TO-BUY, AND CHANGE
Scale to full application
Build or buy, with training and change management

Deep Dive
Identify two drivers
New value-adding activities, or pain-point fixes

How to identify the right use cases?
A 3 MONTHS ENGAGEMENT
© WAVESTONE | 27
Level 2 | Platform renewal, one step at a time
Human-agent teams
AI ≈ 50%
Human ≈ 50%
IGA / PAM
IGA, PAM, machine & agent identities, access governance
Business Continuity
Dependencies, impact analysis, recovery orchestration
Data security
DLP, DSPM, classification, data risk
US Insurance
AI-native GRC
Continuous controls, compliance, TPRM and vendor risk
UK Bank
AI SOC
Detect, investigation, response, threat hunting
AI pentest
Continuous exposure discovery, validation & remediation
Global Manuf.
Global Insurance
CISO Chief Information Security Officer
IAM
RESILIENCE
INFRA SEC
GRC
DEFENSE
SEC BY DESIGN
App security
App security posture management, code & pipeline security
EU manufacturing
Data & AI Office
AI adoption accelerates as platform renewal unlocks cyber ROI at scale. Integrated platforms enable automated context sharing, faster insights, consistent policies and cross-function action
Scaling AI across cyber requires a common approach: Create a Cyber Data & AI Office
© WAVESTONE | 28
AI-FIRST CISO OPERATING MODEL
Automotive experience
21-month program
€3.6M investment
10 FTEs mobilized
40 AI workflows targeted by end-2026
50 AI agents deployed in the SOC
XX tools consolidated
How?
Embed AI by design > Unify platform > Upskill teams > Align staffing, ownership & partners
Deep Dive
LEVEL 2 | PLATFORM RENEWAL
Two approaches, one objective
ENTERPRISE DATA PROTECTION AT SCALE
Insurance experience
XX-year program
$XXX investment
1,500 applications
65,000 collaboration sites
50,000 files shared
40 PB of data
How?
Unify governance, processes & technology > Strengthen data visibility & control > Remediate risk at scale
© WAVESTONE | 29
Level 3 | Cyber at machine speed
Human-led, agent-operated
APIs
AGENTIC AI PLATFORM
Cyber Agents
…
Access rights / DLP
Patching & Config.
EDR / NDR / FW
MCP & APIs
Cyber Data
Lake
Lake


SOC / EDR
CTI / Vuln.
Assets / Configs
GRC / TPRM / Risks
…
1
Use the big to create your CYBER DATA LAKE
› Turn fragmented, slow-moving cyber data into real-time context
› Collect, enrich, and normalize data through APIs
2
Use AGENTIC AI PLATFORM
› Built on existing processes and control models
› Delegate actions with the appropriate level of human oversight
DEFENSIVE
React to incidents, team by team
PROACTIVE
Anticipate drift in real time, act across teams
To operate at machine speed, cyber needs a unified data foundation for agentic operations
© WAVESTONE | 30
Cyber graph (OT / IT) | Data lake + graph · OT stays human-in-the-loop
Level 2 | Platform renewal, one step at a time
Human-agent teams
AI ≈ 50%
Human ≈ 50%
Currently a big changes are occurring, one platform at a time within our client. Large platforms allow automatic bridges such as automated context sharing, faster insights, consistent policies, cross-functional actions. Here are some ideas and examples of platforms that we have developed …
GRC
SEC BY DESIGN
INFRA SEC
IAM
CYBER DEFENSE
RESILIENCE


CISO Chief Information Security Officer
High value cyber //
Data & AI Office
Trust & TokenOps
Good version
Continuous Build : continuous pour adapter les agents et les données
Run : experts in the loop
Check : vérification indépendante de la confiance, de l’efficacité et des couts
CONTROL COST OVER TIME
Keep the platform sustainable as usage scales

PRESERVE TRUST
Keep humans accountable for delegated actions

OBSERVE PERFORMANCE
Know what agents do and how well they perform

› Quality and evaluation
› Reliability and observability
› Decision traceability
› Human oversight
› Ownership and accountability
› Cost management
› Maintenance lifecycle
› Change and model governance
IN THE WORKS
© WAVESTONE | 31
AI ≈ 80%
Human ≈ 20%

SET DECISION RIGHTS
Risk appetite set by the business, escalation thresholds

GOVERN AGENTS
Identity, rights, traceability and audit of every agent

EMBED EXPERTS
Cyber experts inside business, IT and OT teams


GRC agent
Sec-by-design agent
Infra sec agent
IAM agent
Cyber defense agent
Resilience agent
Level 3 | Cyber at machine speed
Human-led, agent-operated
Switch from a defensive to a proactive security position, in real time, using the following golden rules & cyber graph
Cyber graph (OT / IT) | Data lake + graph · OT stays human-in-the-loop
Assets
Identities
Vulnerability
Controls
Third parties
Data
Business processes
DEFENSIVE
React to incidents, team by team
PROACTIVE
Anticipate drift in real time, act across teams
IN THE WORKS
© WAVESTONE | 32
Start focused, demonstrate the shift, then EXPAND
A focused transformation ambition
A transversal team with authority to act
A lighthouse transformation that creates momentum
SET THE AMBITION | Choose where AI should genuinely transform the model
› Identify the workflows where speed or outcomes must change radically
› Define the target level of transformation
› Align Cyber, IT and business leadership on the ambition

BUILD A LIGHTHOUSE | Use one workflow to demonstrate the new model
› Select an end-to-end workflow with visible operational value
› Redesign the workflow, rather than automating isolated tasks
› Use the first results to prepare the next transformations
REORGANIZE THE FLEET | Break silos to scale the transformation
› Bring together Cyber, IT, Data, AI and operational teams
› Establish clear ownership with one executive sponsor and one transformation lead
› Give the transformation team clear decision rights and authority to act
› Redesign roles and responsibilities as AI reshapes how work gets done


Bet on your teams !
Empower the crew to navigate the transformation
IN THE WORKS
© WAVESTONE | 33
01
CYBER
FOR AI
Secure the ecosystem
02
CYBER
AGAINST AI
Reset the
defensive baseline
03
CYBER
WITH AI
Defend at machine speed
> Go beyond technical changes
Transform your organization
© WAVESTONE | 34
02
CYBER
AGAINST AI
Reset the
defensive baseline
01
CYBER
FOR AI
Secure the ecosystem
03
CYBER
WITH AI
Defend at machine speed
02
CYBER
AGAINST AI
Reset the
defensive baseline
01
CYBER
FOR AI
Secure the ecosystem
Go beyond technical changes
Transform your organization
@pauline
© WAVESTONE | 35
Lead the human shift: cyber teams that secure AI and use it
Two goals for every CISO team: secure the company's AI, and put AI to work inside cyber
01
Managing change
• Show the way: leaders use AI in their own daily work first
• Say early which tasks move to agents and which roles grow
02
Training
• AI security basics for every cyber role: prompt injection, agents, data leaks
• Hands-on labs: build and red-team an agent in a sandbox
03
New org chart
• New roles: AI security architect, agent identity owner, AI red teamer
• Rebuild junior paths as L1 tasks shift to agents
04
New accountability
• A named human owner for every agent and its actions
• Shared AI risk with IT, data and business teams (RACI)


A new team:
Cyber Data & AI Office
/ With your own data scientists and AI engineers
/ Build and maintain the Cyber Data Lake & AI agents
/ Upskill and empower all cyber teams through AI literacy
Reprendre commentaires de GBI lors de la présentation
@pauline
© WAVESTONE | 36
QR Code
CYBER AGAINST AI
>
CYBER FOR AI
>
> Dicover an dmange your agents
> Protect your AI platform
> Manage Agent identity
> Secure emerging risks : resilience & open weight=
CYBER WITH AI
>
How do you lead the shift to AI?
BET ON YOUR TEAMS: Empower them to lead the shift
> Upskill teams, give them ownership and break silos to scale
> Enforce the new cyber baseline 24 / 48 / 72
> Take the ownership of defensive actions
> Accelerate cyber teams
> Renew major platfomrs
> Build your cyber graph to go at machine speed
© WAVESTONE | 37